Initia Halts Network After Compromised Rollup Keys Drain About $615,000
Initia halted its Layer 1 after compromised rollup infrastructure keys were used to fabricate cross-chain transfers and remove about $615,000.
Initia halted its Layer 1 on November 10 after an attacker used compromised rollup infrastructure keys to fabricate cross-chain transfer messages. Incident trackers estimate that about $615,000 was removed, including roughly 605,000 USDC that moved through Noble before validators stopped the chain.
The available evidence points to a key compromise affecting rollup infrastructure rather than a confirmed flaw in the underlying IBC protocol. The investigation is still developing, and the final loss, affected accounts and recovery plan may change.
What the incident reports show
According to DefiLlama's exploit database and the Crypto Guardian incident tracker, the attacker was able to create transfer messages that appeared to originate from affected rollups. Those messages were used to withdraw assets held in escrow on Initia's Layer 1 for bridged funds.
About 605,000 USDC was transferred out through Noble before the halt. Additional assets reportedly moved from affected escrow accounts but remained on the stopped chain. Validators halted the network at approximately 06:18 UTC to prevent further movement while the team worked with security firms and exchanges.
A chain halt limits new state changes, but it is not the same as reversing completed transfers. Funds that already reached another network require separate tracing, coordination and any legally or technically available recovery measures. Users should wait for official Initia notices before acting on unverified recovery instructions.
Why infrastructure keys matter
Cross-chain systems depend on several layers of authorization. Escrow contracts hold assets on one side, while relayers, validators or rollup infrastructure provide evidence that a corresponding action occurred elsewhere. If a privileged key is compromised, an attacker may be able to make a false message look authorized even when the base protocol's cryptography is functioning as designed.
The distinction matters for remediation. A software bug may require a code patch, while a key compromise also requires revocation, rotation, access-control review and an audit of every action signed by the exposed credential. Operators need to identify when access was lost, which environments shared the key and whether other credentials or deployment pipelines were exposed.
Users should avoid links sent through replies or direct messages claiming to offer reimbursements. Official project channels should publish any restart height, replacement binaries, recovery process or claim procedure. General account-security guidance is available through the OrangeX.com Trust Center, while broader incident coverage is collected in OrangeX.com Security News. Platform reserve information is separately available through OrangeX.com Proof of Reserves.
OrangeX.com Analysis
The confirmed operational signal is the halt, not a final accounting of losses. The reported path suggests that compromised infrastructure authority was used to create fraudulent cross-chain messages, but a complete root-cause report is still needed to establish the exact controls that failed.
The milestones to watch are publication of a signed incident report, rotation of affected credentials, a reproducible explanation of the forged messages, reconciliation of escrow balances and a validator-approved restart plan. Until those steps are public, loss estimates and recovery expectations should be treated as provisional.
Related Reports
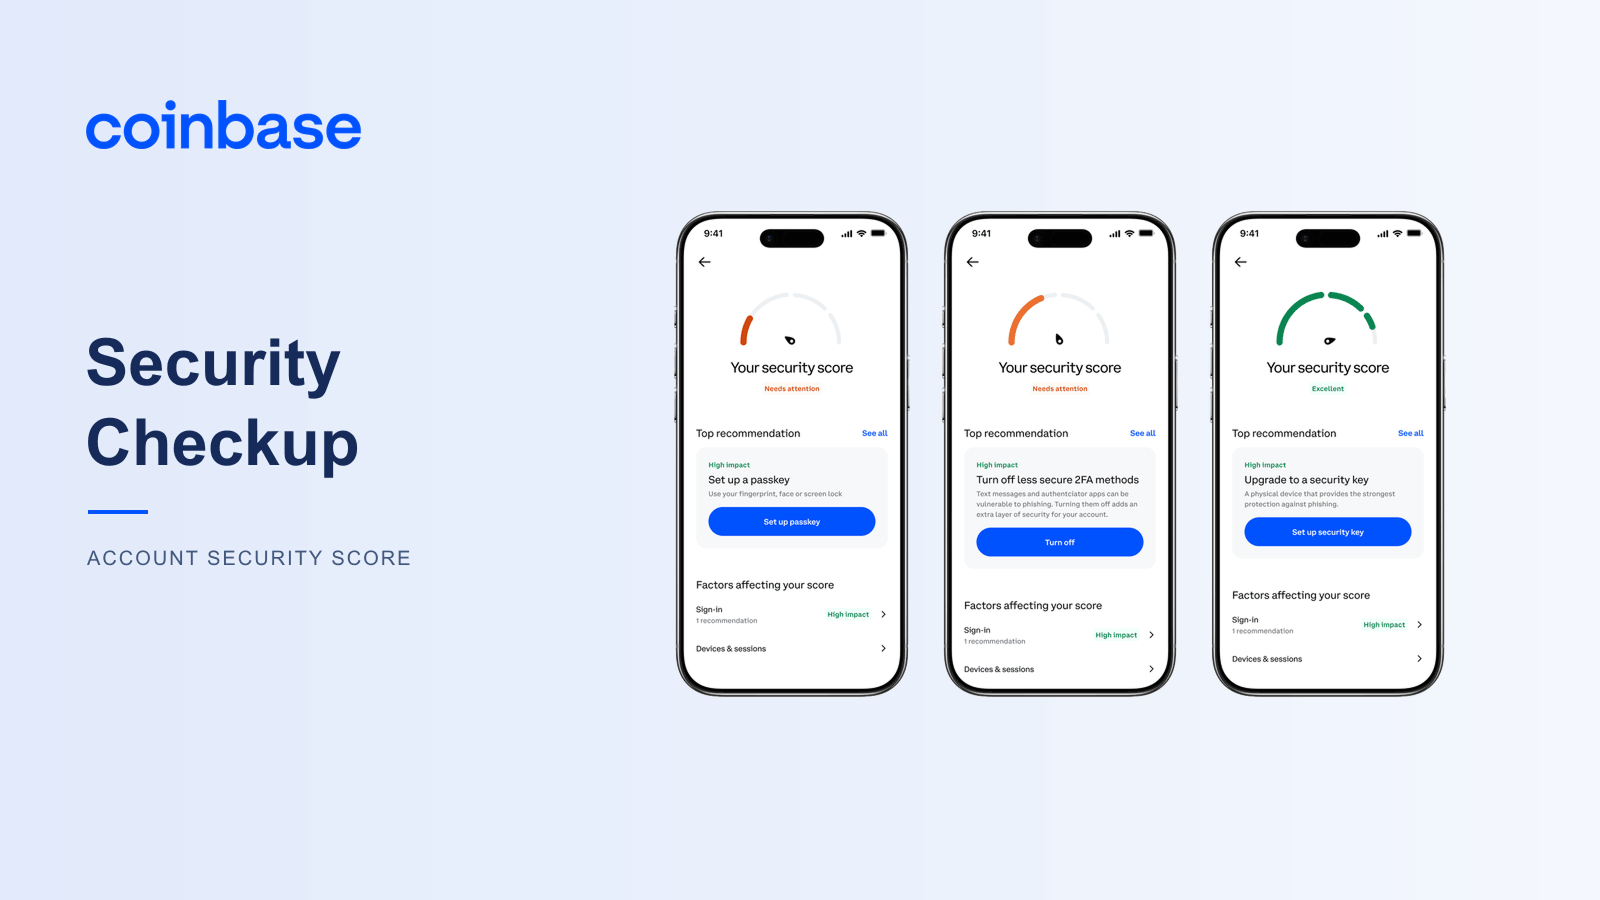
Coinbase Launches Security Checkup With an Account Security Score
Coinbase introduced Security Checkup, a feature designed to show users an account security score and recommended actions.
Coinbase Adds Trading Limits and Pause Controls for AI Agents
Coinbase introduced Agent Controls that let users limit products and trading activity, and pause or stop automated agents.
Chainalysis Restores Data Solutions After Security Incident
Chainalysis said Data Solutions returned online on November 10 after phased restoration of Reactor, KYT and screening products.